Why is a longer password a stronger password?
 The answer, you see, is length.
Because every extra character multiplies the number of possible combinations, making it much harder for a machine to guess the password by trying one after another. The U.S. National Institute of Standards and Technology (NIST) also says length is a primary factor in password strength.
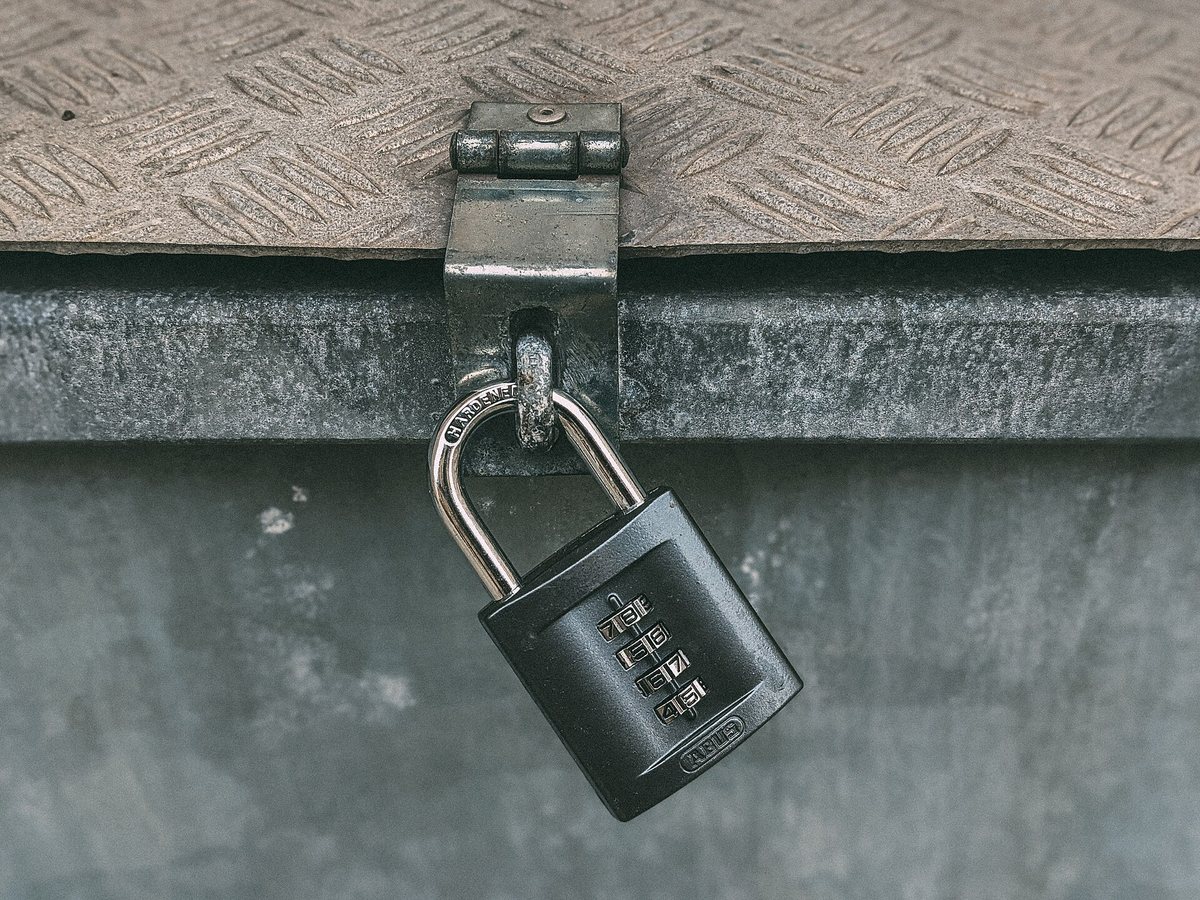
One more character multiplies the combinations
When you add 1 character to a password, the number of combinations is multiplied by the number of different characters that could go in that spot. The head of information security at Chapman University also explains that each added character multiplies the possible combinations, making a brute-force attack (trying every combination in turn) less likely to succeed.
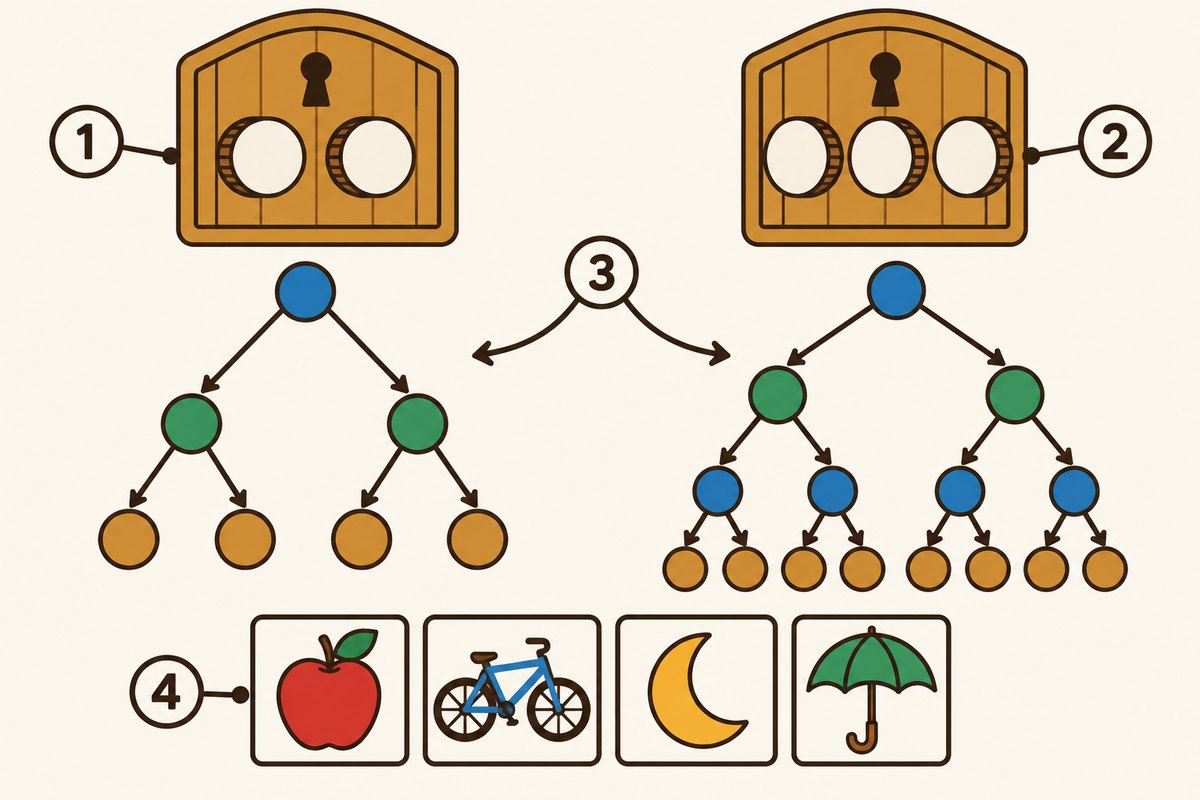
- 1A lock with two dials (a short password)
- 2A lock with three dials (a longer password)
- 3The number of paths to try multiplies with each extra place
- 4A long passphrase made of unrelated words
Length matters more than symbols
NIST's guidelines (SP 800-63B) say that length is a primary factor in password strength. They also point to research showing that when people are forced to mix in capital letters or symbols, many make predictable changes, such as turning "password" into "Password1!". So the current guidelines tell services not to require mixtures of different character types.
Recommended lengths differ a little by agency
How long is long enough? It differs a little from agency to agency. NIST requires at least 15 characters when a password alone is used to log in, and at least 8 characters even when it is combined with another way of checking who you are. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) recommends at least 16 characters, and Japan's ministry recommends, ideally, a fairly long random string of letters and numbers of 10 or more characters.
Long but easy to remember
To remember a long password, Japan's ministry suggests joining several unrelated English words that don't form a sentence, or putting numbers between them. CISA also gives the example of a "passphrase" made of 4 to 7 unrelated words, and recommends a "password manager," a program that creates, stores and fills in your passwords for you.
Don't reuse passwords
No matter how long it is, try not to reuse the same password on several services, the ministry advises. On the other hand, it says there is no need to change passwords regularly unless there is a worry such as a leak. NIST also tells services not to require regular changes, but to have a password changed when there is evidence it has been leaked.
Want to know more?
- NIST recommends that services allow passwords of at least 64 characters.
- Under NIST's guidelines, new passwords are checked against a list of commonly used or leaked passwords, and ones on the list can't be used.
- NIST requires services to allow password managers and autofill.
Quick quiz: test yourself
Remember what you just read? Give it a try!What is a primary factor in password strength?
Show the answer
- Always including symbols
- Changing it regularly
- The password's length
The password's length NIST's guidelines say length is a primary factor in password strength, because each extra character multiplies the number of combinations.
NIST's guidelines say length is a primary factor in password strength, because each extra character multiplies the number of combinations.
Next quiz ›Sources
- NIST Special Publication 800-63B: Digital Identity Guidelines, Authentication and Authenticator ManagementNational Institute of Standards and Technology (NIST)
- Use Strong PasswordsCybersecurity and Infrastructure Security Agency (CISA)
- 推測できる簡単なパスワードを利用しないようにしよう(国民のためのサイバーセキュリティサイト)総務省 (in Japanese)
- The Long and Short of It: Why Password Length MattersChapman University, Information Systems & Technology
This article was written after checking the sources above as of 2026-10-03. Explanations may change as research progresses. Photo credits are shown below each photo.
Next fun fact ▶
 TechnologyWhat does the "I'm not a robot" checkbox look at?"I'm not a robot." What can a single click on that box really tell?
40 surprising animal facts with big photos and short, easy text. A fun-facts book for kids and grown-ups to read together.
See it on Amazon